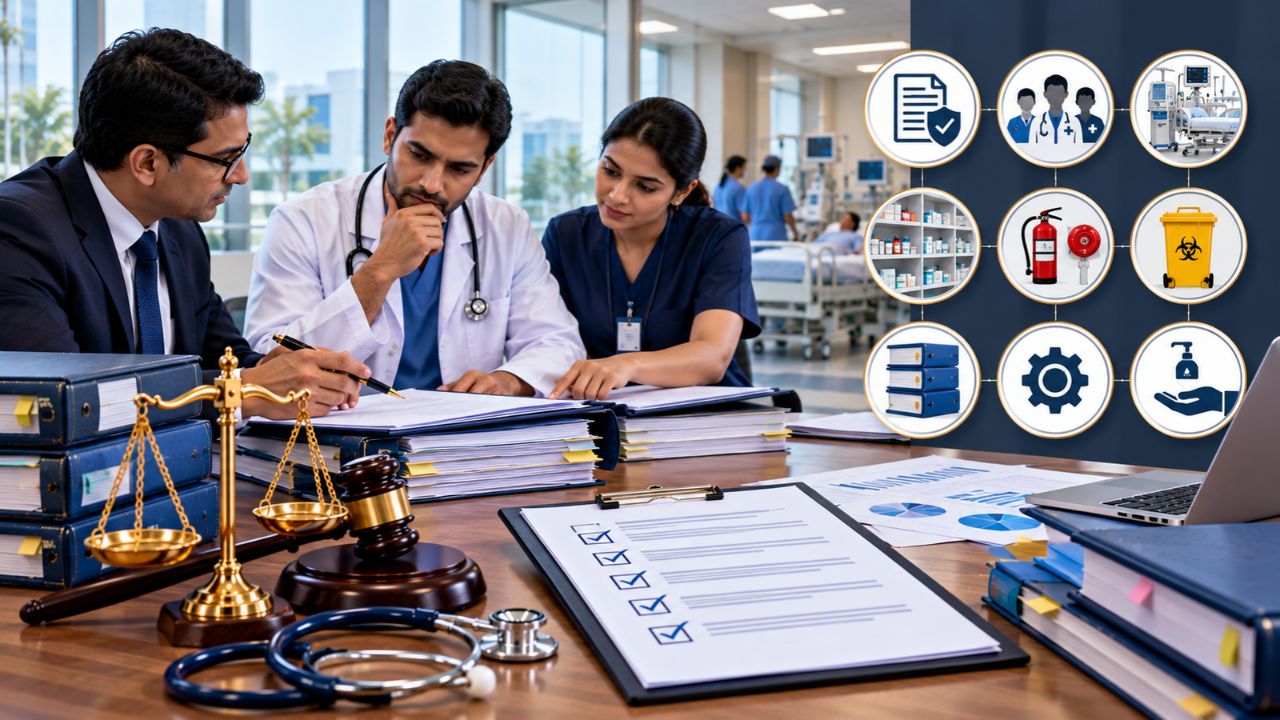
A hospital compliance audit in India helps management identify legal, regulatory and operational gaps before an inspection by a health authority or other regulator. It examines whether the hospital holds the required licences, maintains accurate records, follows patient safety procedures and meets the legal requirements applicable to its location and services.
Hospitals face obligations across several areas, including clinical establishment registration, fire safety, biomedical waste management, medical records, staffing, pharmacy operations and specialised diagnostic services. Missing a renewal, maintaining incomplete records or failing to follow an approved procedure can result in regulatory action, financial penalties or disruption to services.
A well planned audit allows hospital owners and administrators to identify weaknesses, assign corrective actions and demonstrate a genuine commitment to compliance. It should assess not only whether documents exist, but also whether the hospital follows the procedures those documents require.
What Is a Hospital Compliance Audit?
A hospital compliance audit is a structured review of the laws, licences, policies and operational controls governing a healthcare facility. It may be conducted internally by management or compliance staff, or externally with support from legal, clinical and technical professionals.
The audit should cover both documentary compliance and actual practices. For example, a hospital may hold a valid fire safety approval but still have blocked emergency exits. Similarly, it may have a biomedical waste management agreement but fail to segregate waste correctly at the point of generation.
An effective audit tests whether the hospital’s daily operations match its legal obligations and documented procedures. It should also identify who is responsible for each requirement and how management will verify ongoing compliance.
Review Hospital Registration and Operating Licences
The first step is to verify the hospital’s legal authority to operate. Depending on its location, the facility may need registration under the Clinical Establishments (Registration and Regulation) Act, 2010 or the relevant state legislation governing hospitals and nursing homes.
The central Act does not apply uniformly across India. Management must confirm which legislation applies in the relevant state or Union Territory and whether any local registration requirements also apply.
The audit should examine the registration certificate, approved facility category, permitted services, renewal requirements and any conditions imposed by the competent authority. The hospital should also verify whether changes to ownership, premises, bed capacity or clinical services require notification or fresh approval.
Management should maintain a central register of licences showing the issuing authority, validity period, renewal deadline and responsible department. This makes it easier to identify expired approvals before an inspection.
Check Fire Safety, Building Approvals and Emergency Preparedness
Fire safety and building compliance are essential areas of a hospital audit. Healthcare facilities may accommodate patients who cannot evacuate independently, making emergency planning particularly important.
Management should verify applicable building approvals, occupancy permissions and fire safety clearances. The audit should also assess whether emergency exits are accessible, evacuation routes are clearly marked, fire equipment is maintained and relevant staff know their responsibilities.
Fire drills, equipment inspection records and emergency response procedures should be reviewed. Any deficiencies identified during previous inspections should have documented corrective actions.
The audit should also examine emergency preparedness beyond fire incidents. Depending on the facility, this may include evacuation procedures, backup power, oxygen supply continuity, emergency communication and arrangements for managing critical patients during service disruptions.
A valid certificate alone is not enough. Hospital management should confirm the facility continues to meet the conditions and safety standards applicable to it.
Examine Biomedical Waste Management
Biomedical waste management is another priority. The Bio Medical Waste Management Rules, 2016 establish requirements for handling biomedical waste, subject to the applicable provisions and amendments.
The audit should review the hospital’s authorisation from the relevant State Pollution Control Board or Pollution Control Committee, where required, along with agreements with authorised waste treatment providers.
Management should check whether waste is segregated correctly, labelled where required, stored safely and collected according to the applicable procedures. Records of waste quantities, collection, handover and staff training should also be examined.
The audit should pay particular attention to practical implementation. Incorrect segregation, unsafe storage or incomplete records may indicate wider weaknesses in staff training and supervision.
Where deficiencies are identified, the hospital should document the corrective action, responsible person and completion date. Staff should receive additional training where necessary, with follow up checks to confirm the problem has been resolved.
Verify Specialised Service Approvals
Hospitals providing specialised services may need additional registrations or permissions. The exact requirements depend on the equipment, treatment and activities carried out at the facility.
Radiology and certain radiation related services may require approvals from the Atomic Energy Regulatory Board. Facilities conducting regulated prenatal diagnostic procedures must review their obligations under the Pre Conception and Pre Natal Diagnostic Techniques Act, 1994. Blood banks, pharmacies, organ transplantation services and other specialised units may also require specific licences or registrations.
The audit should compare the services actually offered with the permissions held. Management should check whether equipment, premises, personnel and operating procedures meet the applicable conditions.
It is also important to review expiry dates, inspection reports and records of regulatory correspondence. Where a service has been introduced recently, management should confirm all necessary approvals were obtained before it began operating.
Hospitals should not assume the main hospital registration automatically covers every specialised department.
Assess Medical Staff Credentials and Employment Records
Hospitals should verify whether doctors and other regulated professionals hold the qualifications and registrations required for their roles. The audit should examine credential records, professional registrations, appointment letters, job descriptions and relevant training records.
Management should also check staffing levels against applicable requirements and the hospital’s actual service commitments. Where personnel are supplied by contractors, the audit should establish whether contractual arrangements and statutory obligations are being met.
Employment compliance may include applicable wage requirements, statutory contributions, working conditions, workplace safety and records required under relevant labour laws. The exact obligations depend on the establishment, workforce and legal framework in force.
Staff records should be complete, current and accessible to authorised personnel. Missing credentials, expired registrations or unclear reporting responsibilities should be treated as compliance gaps requiring prompt attention.
Review Patient Records, Consent and Clinical Procedures
Medical records provide important evidence of the care delivered and the procedures followed. The audit should examine whether records are accurate, complete, secure and maintained for the periods required by applicable law and professional standards.
Management should review patient registration, clinical notes, diagnostic reports, discharge summaries, consent forms and referral records. It should also assess whether staff follow the hospital’s procedures for correcting records and managing access.
Consent processes deserve particular attention. The hospital should confirm appropriate consent is obtained and documented for relevant procedures, with suitable explanations provided to patients or authorised representatives.
The audit should also examine incident reporting, clinical complaints, infection control, medication management and adverse event reviews. Policies must reflect actual practice, and staff should understand when an incident must be escalated.
Examine Pharmacy, Medicines and Equipment Controls
Hospitals operating pharmacies or handling regulated medicines should verify the applicable licences, storage arrangements and record keeping requirements. The audit should assess whether medicines are stored under appropriate conditions, expiry dates are monitored and restricted medicines are handled according to applicable law.
Procurement and inventory records should be reconciled where appropriate. Management should investigate unexplained stock differences, expired medicines and gaps in temperature monitoring for products requiring controlled storage.
Medical equipment also requires attention. The hospital should maintain service records, calibration documents where applicable, preventive maintenance schedules and evidence of corrective action when equipment fails.
For critical equipment, management should confirm backup arrangements are available where required and staff know how to report faults. Equipment records should help demonstrate safe operation rather than simply show a maintenance contract exists.
Check Patient Information, Data Protection and Confidentiality
Hospitals handle sensitive information through paper records, electronic medical records, billing systems, diagnostic platforms and third party applications. The audit should examine who can access patient information and whether access is appropriate to each person’s role.
Management should review confidentiality policies, user access permissions, password controls, backup procedures and incident response arrangements. It should also assess how information is shared with laboratories, insurers, technology vendors and other service providers.
The Digital Personal Data Protection Act, 2023 and its applicable commencement provisions and rules should be considered when assessing obligations involving digital personal data. Other relevant legal, contractual and professional confidentiality requirements may also apply.
The audit should check whether data retention and disclosure practices follow the applicable framework. It should also test whether the hospital can identify, investigate and respond to suspected data breaches.
Review Contracts, Insurance and Regulatory Correspondence
Compliance responsibilities often extend beyond licences and clinical records. Hospitals should review agreements with outsourced laboratories, waste treatment providers, security agencies, housekeeping contractors, ambulance operators and technology suppliers.
The review should confirm the services are properly documented and the contracts allocate responsibilities for safety, staffing, records, incident reporting and regulatory cooperation. Management should verify relevant licences and insurance cover where required.
The hospital should also maintain an organised record of inspection reports, notices, complaints, responses and corrective actions. Any unresolved issue should have a named owner, a deadline and evidence of progress.
Ignoring a regulatory notice or failing to comply with a previous direction can increase the risk of further action. Management should therefore ensure correspondence is escalated promptly to the appropriate decision makers.
Prepare a Corrective Action Plan Before Inspection
An audit is useful only when its findings lead to action. Once the review is complete, management should classify each gap according to its seriousness, legal significance and potential impact on patient safety.
Urgent issues should be addressed first. These may include an expired mandatory approval, unsafe equipment, serious fire safety deficiencies or improper handling of biomedical waste.
Each finding should identify the requirement involved, the evidence reviewed, the corrective measure, the responsible person and the target completion date. Management should retain proof of completion and arrange follow up verification.
Hospital leadership should receive a clear summary of significant risks and unresolved matters. Where specialist interpretation is needed, the hospital should obtain appropriate legal or technical advice rather than assume an uncertain requirement does not apply.
Engaging healthcare compliance lawyers can help management interpret applicable laws, review licences and assess whether corrective measures adequately address legal exposure.
If an inspection results in a show cause notice, proposed penalty or other contested regulatory action, regulatory dispute resolution lawyers can assist with reviewing the notice, preparing a reasoned response and evaluating available remedies.
Conclusion
A hospital compliance audit in India should provide management with a clear picture of legal obligations, operational weaknesses and outstanding risks before an inspection takes place. Registration, safety approvals, waste management, staff credentials, clinical records, specialised services and data protection all deserve careful review.
The strongest approach combines accurate documentation with practical verification. By assigning responsibility, correcting deficiencies and retaining evidence of action, hospitals can improve compliance readiness and support safer, more reliable patient care.
Frequently Asked Questions
Q1: How often should a hospital conduct a compliance audit?
Hospitals should establish a regular audit schedule based on their services, risk profile and legal obligations. High risk areas may require more frequent checks, while additional reviews are advisable before inspections, service expansions or licence renewals.
Q2: How often should a hospital conduct a compliance audit?
Hospitals should establish a regular audit schedule based on their services, risk profile and legal obligations. High risk areas may require more frequent checks, while additional reviews are advisable before inspections, service expansions or licence renewals.
Q3: How often should a hospital conduct a compliance audit?
Hospitals should establish a regular audit schedule based on their services, risk profile and legal obligations. High risk areas may require more frequent checks, while additional reviews are advisable before inspections, service expansions or licence renewals.
Q4: Which licences should a hospital check before an inspection?
The required approvals depend on the location and services offered. Common areas include hospital registration, fire safety, biomedical waste, pharmacy operations and specialised diagnostic or treatment services.
Q5: Who is responsible for hospital compliance?
Responsibility is shared across hospital leadership and relevant departments according to their roles and the applicable law. Management should appoint clear owners for each requirement while ensuring statutory obligations are met.
Q6: What happens if a hospital fails a compliance inspection?
Consequences depend on the breach and the relevant legal framework. They may include directions to correct deficiencies, penalties, restrictions on services or other regulatory action. The hospital should review the findings promptly and respond within applicable deadlines.
Q7: Can a hospital use an internal checklist instead of an audit?
A checklist is useful, but it may not reveal whether controls work in practice. A proper audit tests documents, operational procedures and evidence of compliance, with corrective actions recorded and verified.